
AI Detection in B2B Content: A Practical QA Workflow for Cybersecurity Teams
It’s hard to argue the fact that the adoption of AI technology has fundamentally reshaped the content landscape and made it possible to produce large volumes of text, images, and video faster than ever. Even though it made the lives of many B2B marketers easier, it also brought a new set of cybersecurity risks because AI-generated content is a potential vector for sophisticated phishing campaigns.
A single piece of content with misleading security recommendations can damage client relationships and undermine years of carefully built credibility. Misinformation and disinformation ranked as the top short-term global risk in the World Economic Forum's Global Risks Report 2025, with AI-generated content cited as a leading driver (World Economic Forum, retrieved 2026-09-19). Cybersecurity teams carry more exposure than most, because the content they publish doubles as a security recommendation someone may act on.
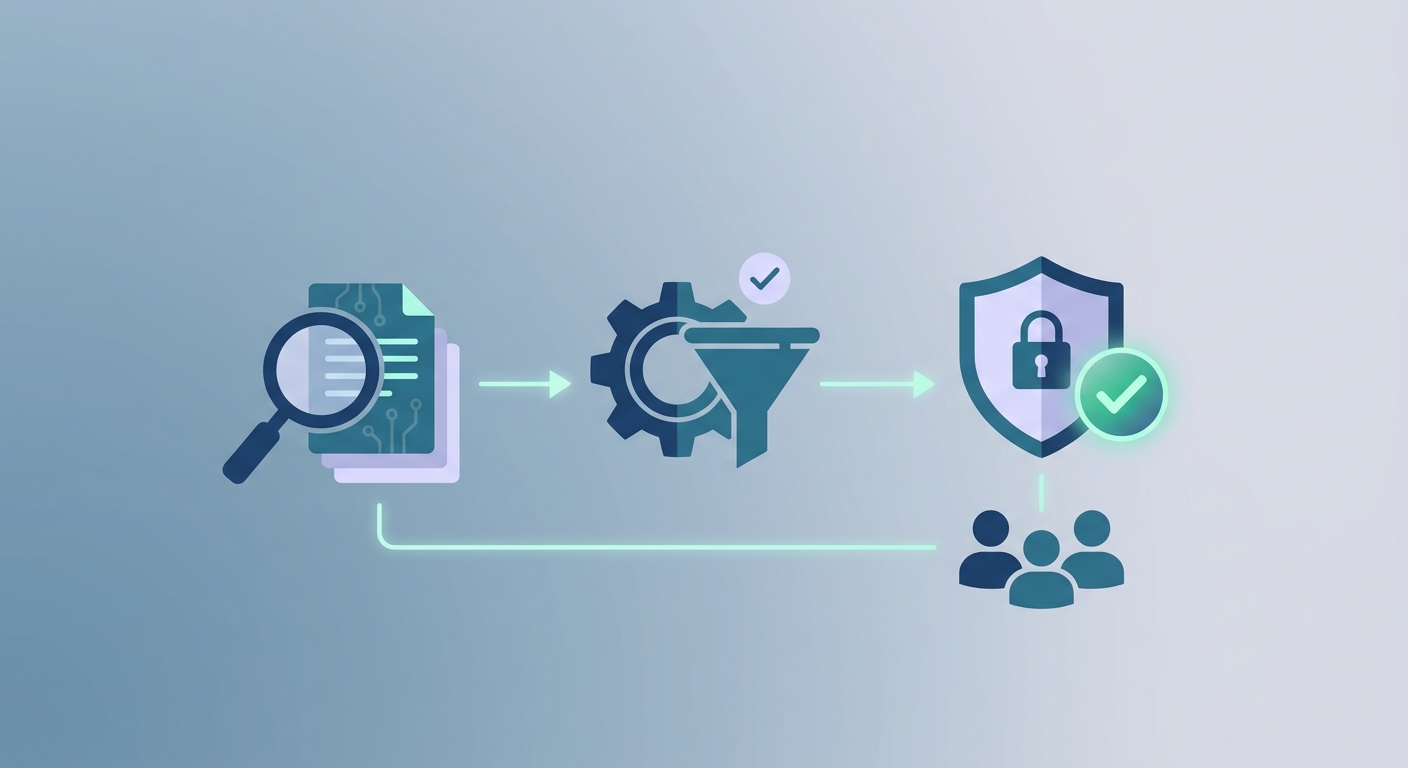
That's why cybersecurity teams increasingly pair an AI detection tool with a defined, step-by-step QA workflow, rather than relying on either one alone. A detector flags content that warrants a second look; the workflow determines what happens next. That combination — not the detector score by itself — is what this article walks through.
Why is it a Cybersecurity Risk?
Let’s look closer at the two building blocks of cybersecurity today: trust and real-time accuracy. Unfortunately, AI-generated content can compromise both these features. Phishing emails, for example, can be highly personalized to bypass traditional spam filters and trick even savvy employees.
Beyond email, an AI-generated blog post on a compromised website could contain a convincing but fake case study that tricks them into downloading malware. The speed and volume at which this content can be produced make it nearly impossible for manual human review to keep up.
On top of that, AI-generated technical content often lacks the nuanced understanding of specific client environments that human experts provide. The absence of AI content detection leads to generic recommendations that may not address unique security challenges.
Furthermore, the risk extends to intellectual property. If employees use public AI tools with confidential company data, they could expose sensitive information. As you very well know, data leaks and compliance violations are the two things every cybersecurity team wants to avoid.
We should also mention the possible financial implications. Cybersecurity is the industry where even one single mistake could result in client lawsuits and reputation damage that far exceeds the cost of implementing a content approval workflow.
The Practical QA Workflow Framework
Now that we’ve established the most frustrating consequences of using AI-generated content, we can move on to the step-by-step guide on how to avoid this unpleasant experience.
Step 1: Initial Screening
No matter if it's a blog post from a freelance writer or a marketing email draft, your cybersecurity team must review this content with the help of a reliable AI detection tool. Alternatively, they can implement a multi-tool approach (we will expand on this topic later) that includes specialized technical writing analysis.
While not foolproof, these tools can quickly flag content that has common AI-generated patterns, such as predictable sentence structures or a lack of a unique brand voice. After that, it becomes possible for human reviewers to focus on content that requires a deeper analysis.
Step 2: Human Review Process
This is the most critical part of the workflow that requires you to combine automated checks with expert human judgment.
Semantic and Contextual Review
This is where the team scrutinizes the content's meaning and intent to ensure it makes logical sense within the company's established narrative. A suspicious call-to-action or a link to a seemingly irrelevant topic can be a significant red flag.
Technical Inspection
At this stage, the team must inspect the underlying technical components of the content, including scanning all embedded URLs for known malicious domains. Note that even images can be a threat.
Source Analysis
It’s crucial to confirm that cited threat intelligence comes from reputable sources and that technical procedures have been tested in relevant environments. In addition, a sudden shift in a long-time collaborator's writing style could also be an indicator of a compromised account.
Step 3: Human Expertise
As we’ve already mentioned, no AI-generated content checker can replace the profound understanding of a human expert. Therefore, a senior cybersecurity professional must conduct a final review, which includes spotting an unnatural tone, the presence of outdated information, and any links that do not align with the company's digital properties. Fixing a flagged tone is a separate exercise from catching it — see our guide on making AI content sound human without losing technical accuracy for techniques that address flagged tone issues without reintroducing inaccuracy.
Step 4: Documentation and Feedback Loop
The final stage involves documenting review decisions and creating feedback loops that help improve both automated screening parameters and human review criteria. If the content fails the review, the cybersecurity team’s task is to investigate this case in detail and document their findings for future use.
Additional Practical Recommendations
If your team goes for a multi-tool approach, here is a list of helpful instruments that have proved to be a valuable addition to human expertise.
An AI text detector can serve as a useful first filter to flag content for deeper review.
URL/domain scanners like VirusTotal and Google Safe Browsing are essential for checking the reputation and safety of any embedded links.
Code scanners integrated into a content management system can help your team identify unusual scripts.
Building an internal database of known malicious sources and common AI-generated content patterns can help your team create a more effective defense over time.
When choosing a tool, you should look for ones that let you change the detection parameters for technical content and give you detailed reports that help you keep improving your process. Also, make sure to allocate enough budget resources for both technology costs and the human support required for effective review processes. On the publishing side of the same pipeline, plain-English test automation can cover the functional checks — broken links, missing metadata, template regressions — that a human-review workflow like this one isn't built to catch at scale; see ensuring quality in AI-generated SEO content with test automation.
One more point to keep in mind is that there should be clearly defined team roles, where every AI detection specialist understands both cybersecurity content requirements and AI detection technologies.
Why This QA Workflow Also Protects Your AI Search Visibility
A QA process built to catch AI-generated errors has a second benefit beyond risk avoidance: it protects the accuracy of the content AI answer engines cite when they recommend your brand. ChatGPT, Perplexity, and similar tools increasingly surface cybersecurity vendors directly inside their answers, and they draw on the same published content this workflow is reviewing.
Content that passes a rigorous QA process — accurate claims, verified sources, no hallucinated recommendations — is also the content most likely to earn a citation instead of a correction. A factual error that slips through doesn't just risk a client relationship; once an AI model has ingested it, it can keep surfacing in answers long after the original post is fixed. GrackerAI's AI visibility tracking can help cybersecurity marketing teams see whether an AI model is describing their brand or products inaccurately, which is often the first sign that something in the content pipeline needs a closer look.
Frequently Asked Questions
Can AI detection tools reliably tell if content was written by AI?
Not with certainty. AI detectors measure statistical patterns like predictable word choice and consistent sentence structure, which correlate with AI-generated text but aren't proof of it. Highly technical or heavily templated human writing can also trigger a high AI-probability score, which is why a flagged score should route content to human review rather than trigger automatic rejection.
How much of the QA process can realistically be automated?
The initial screening and technical inspection steps — running a detector, scanning URLs, checking for malicious scripts — automate well. Semantic review, source verification, and the final expert sign-off require human judgment, particularly for cybersecurity content where a subtly wrong technical recommendation can be more damaging than an obviously wrong one.
What's the biggest mistake cybersecurity teams make with AI-generated content?
Treating an AI detection tool's "pass" as equivalent to a fact-check. A detector can only assess whether text resembles AI output — it says nothing about whether the security recommendations inside that text are accurate, current, or appropriate for a specific client's environment.
Does this workflow apply to internal content, or only client-facing material?
Both, though the review depth should scale with risk. Client-facing security recommendations and technical documentation warrant the full four-stage process; lower-stakes internal content can often skip the source-analysis and senior-expert steps.
What Are Your Next Steps?
The four-stage workflow above gives cybersecurity teams a practical framework for catching AI-generated errors before they reach a client, but it only works if it's run consistently rather than treated as a one-time setup. Teams hesitant to invest in a full pipeline can start narrow: apply the framework to the single highest-risk content type first, then expand once the process is proven out.
Start with a current-state assessment: have your cybersecurity team audit their existing content creation process and flag the highest-risk content types — anything with specific technical recommendations, compliance guidance, or incident-response steps — for review under this framework first.


