IoT Cybersecurity Marketing: How Security Companies Can Build AI-Visible Content
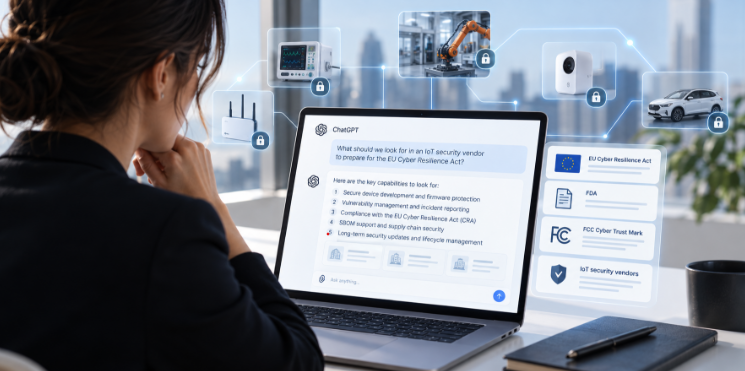
A product security lead at a medical device company opens ChatGPT and types: "What should we look for in an IoT security vendor to prepare for the EU Cyber Resilience Act?" A few seconds later she has a structured answer: a list of capabilities, a handful of named vendors, and links to the sources the model drew from. She hasn't visited a single vendor website yet, but her shortlist is already forming.
That scenario is becoming routine. Gartner predicted that traditional search engine volume would drop 25% by 2026 as users shift to AI chatbots and virtual agents, and technical B2B buyers are among the earliest adopters. For IoT security companies, this changes the marketing question. It's no longer only "do we rank on page one?" but "when an AI assistant explains IoT security to our buyer, are we part of the explanation?"
Here's how security companies can build content that AI systems understand, trust, and cite.
Why IoT security buyers are a special case
IoT security is an unusually good fit for AI-assisted research, and an unusually hard category to market.
The questions are complex and specific. Buyers aren't searching "IoT security." They're asking how to implement secure boot on a constrained microcontroller, what the CRA requires for vulnerability handling, or how to secure OTA updates for a fleet of devices already in the field. Those multi-part questions are exactly where AI assistants outperform a list of blue links.
The buying committee is mixed. A single deal may involve firmware engineers, a product security team, compliance officers, and procurement. Each asks different questions, and AI answers increasingly serve as the shared starting point for all of them.
Regulation is creating a wave of new questions. The EU Cyber Resilience Act's reporting obligations for manufacturers apply from September 2026, with full requirements from December 2027. The FDA expects cybersecurity documentation, including SBOMs, for connected medical devices. The FCC's U.S. Cyber Trust Mark program introduces a security label for consumer IoT products. Every one of these frameworks generates thousands of "what does this mean for us?" queries, and the vendors that answer them clearly are the ones AI models learn to reference.
What makes content "AI-visible"
Generative engines don't rank pages the way classic search engines do. They synthesize answers from sources they consider relevant and credible. While no one outside the model providers knows the exact mechanics, several content properties consistently help:
Entity clarity. Your company should be described the same way everywhere: what you do, for whom, and in which category. If your website calls you an "IoT security platform," your LinkedIn says "device trust company," and press coverage says "cybersecurity startup," models get a blurry picture.
Specificity over generality. Content that explains how something works, with concrete steps, trade-offs, and terminology, gives models material to quote. Generic "IoT security matters more than ever" posts give them nothing.
Answer-first structure. Clear headings phrased as questions, short definitional paragraphs, comparison tables, and FAQ blocks make it easier for AI systems to extract and attribute information.
Original evidence. Vulnerability research, anonymized incident data, or survey results that exist nowhere else turn your brand into a necessary citation.
Third-party corroboration. Mentions in industry publications, standards discussions, and partner content signal that your claims are recognized beyond your own domain.
Map your content to the IoT attack surface
The most effective IoT security content strategies organize around the layers where buyers actually worry, then answer the questions each layer raises:
Layer | Typical buyer questions | Content formats that work |
Device hardware | How do we protect keys on the device? What is a hardware root of trust? | Explainers, architecture diagrams |
Firmware | How do we implement secure boot? How do we sign and encrypt updates? | Technical guides, checklists |
Connectivity | Which protocols are safe? How do we authenticate devices to the network? | Protocol comparisons, glossaries |
Cloud and APIs | How do we secure device management platforms? | Reference architectures, case studies |
Lifecycle and compliance | What does the CRA require? How do we produce an SBOM? | Regulation explainers, templates |
This map does two jobs. It shows which buyer questions you already answer, and it reveals the gaps where competitors, or nobody, currently own the answer. In many security companies' content libraries, the thinnest layer is the one closest to the hardware.
Firmware security: the content gap worth owning
Most cybersecurity marketing concentrates on networks, cloud, and endpoints. Firmware, the low-level code that boots a device and controls its hardware, gets far less coverage, even though it's where many IoT compromises begin and where regulations like the CRA place direct responsibility on manufacturers.
That imbalance is an opportunity. When a buyer asks an AI assistant how to secure device firmware, the model needs sources that explain the topic in practitioner terms. Strong firmware security content typically covers:
Secure boot, where each stage of the boot process cryptographically verifies the next, so unsigned or tampered code never runs
Firmware encryption, which protects intellectual property and makes reverse engineering and cloning harder
Device authentication and encrypted communication, so only trusted devices can connect and data stays protected in transit
Secure OTA updates, with signed packages, integrity checks, and rollback protection, because a device that can't be patched safely remains vulnerable for its entire service life
Security assessments, including code review, penetration testing, and fuzzing at the firmware level rather than only in the companion app
To write about these topics credibly, security marketers should learn the vocabulary engineering teams use. Studying how device engineering specialists describe their work is a practical shortcut. The way firmware engineers at Yalantis define their security scope, for example, covers firmware encryption, secure boot, security assessments, authentication and encryption, and secure OTA updates as core parts of firmware development rather than optional extras. That framing mirrors how technical buyers think about the problem: security is built into the device during development, not bolted on afterward. Content that uses the same language is more likely to match the technical questions buyers put to AI assistants, and more likely to be trusted by the engineers who read it.
Firmware is also a natural place for co-created content. Security vendors and device engineering firms see the same problem from different sides, one from threat detection and the other from secure implementation. Joint guides, webinars, or reference architectures give both parties a stronger, more complete answer than either could publish alone, and create the kind of cross-domain corroboration AI systems value.
Formats that tend to earn AI citations
Some content types consistently punch above their weight in generative answers:
Regulation explainers with practical checklists. "What the CRA means for IoT manufacturers" is searched, and asked, constantly. Make yours the clearest version, updated as implementation guidance evolves, with a dated changelog so models and readers can see it's current.
Glossaries built for the category. Short, precise definitions of terms like root of trust, SBOM, secure element, or attestation are easy for models to extract and attribute. A well-structured glossary can become a frequently cited reference.
Original research. An annual report on IoT vulnerability trends, firmware update practices, or device security maturity gives journalists, analysts, and AI systems a reason to name you. Even a modest dataset, if it's unique and methodologically honest, can outperform dozens of opinion posts.
Comparison and "how to choose" pages. Buyers ask AI assistants to compare approaches and vendors. Balanced comparison content, including honest notes on when your solution isn't the right fit, tends to be treated as more credible than pure promotion.
Technical deep dives signed by real practitioners. Named authors with verifiable expertise strengthen trust signals for both human readers and AI systems.
Get mentioned where models look
Your own website is only part of the picture. Generative engines draw on a broad web of sources, so AI visibility depends on distribution as much as creation:
Contribute articles to industry publications your buyers already read
Participate in standards and working group discussions, and publish summaries of what you learn
Share tools, scripts, or test suites on GitHub, where technical audiences and crawlers both look
Keep your company description consistent across directories, analyst profiles, and partner pages
Earn mentions in podcasts, conference talks, and community forums with real technical substance
Each credible mention reinforces the association between your brand and the problems you solve.
Measure AI visibility, not just rankings
Traditional SEO metrics don't capture whether AI assistants mention you. Security marketers are adding a new layer of measurement:
Prompt tracking: regularly test the questions your buyers ask, such as "best IoT firmware security tools" or "how to comply with the CRA for connected devices," across ChatGPT, Perplexity, Gemini, and Claude
Share of AI voice: how often your brand appears in answers compared with competitors
Citation tracking: which of your pages are linked as sources, and which topics generate no mentions at all
Downstream signals: branded search volume, direct traffic, and prospects who say they "found you through ChatGPT"
Manual testing works at first, but results vary between sessions and models, so platforms that automate AI visibility tracking are becoming part of the security marketing stack.
Be the answer before the RFP arrives
IoT security buyers are forming shortlists earlier than ever, often inside an AI conversation that no vendor gets to join. The companies that show up in those conversations are the ones that answer real technical questions clearly, cover the layers competitors ignore, especially firmware and secure device development, and build a consistent, corroborated presence across the web.
Start with the questions your sales engineers answer every week. Turn them into precise, well-structured content. Fill the firmware gap. Then measure whether AI assistants are starting to explain IoT security the way you do. When they are, your marketing is working in the place where your buyers now begin.